
Kaspersky again passes SOC 2 audit of its antivirus database development process
An independent auditor reviewed controls from August 2025 to July 2026 and found Kaspersky's antivirus database development for Windows and Unix protected against tampering.
Staff Correspondent
Cybersecurity company Kaspersky says the processes it uses to develop, test and release its antivirus databases have again passed a SOC 2 Type II audit. The independent auditor found these processes protected against unauthorised changes and tampering.
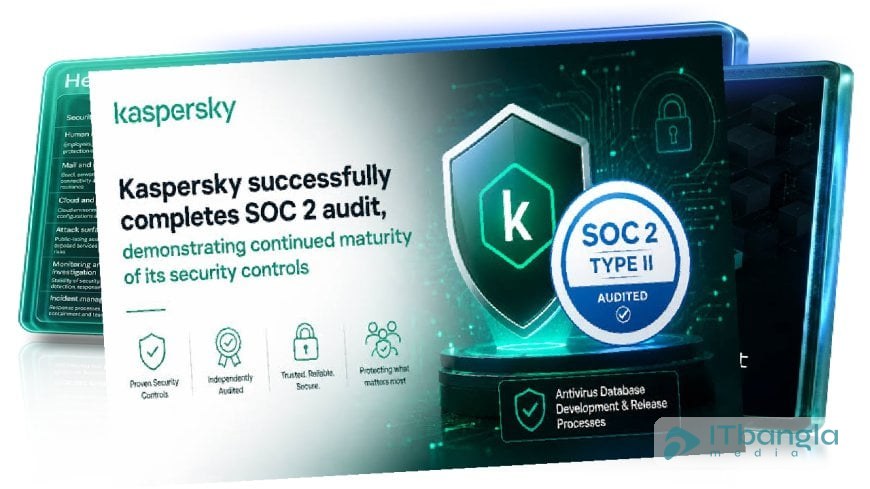
According to a press release published on Kaspersky’s website on 4 September, the audit covered August 2025 to July 2026 and the full lifecycle of antivirus database development for Windows and Unix operating systems. Bangladeshi technology news site Digibangla Tech News reported the news on the afternoon of 15 November.
What the auditor checked
Kaspersky says the auditor tested the design and operating effectiveness of its controls in four ways:
- interviews with management and technical teams;
- observation of procedures in operation;
- review of policies, workflows and control evidence;
- re-performance of manual controls by the auditor.
The auditor concluded that the database development, testing and release processes continue to meet SOC 2 requirements. The company says the full audit report is available on request.
What a SOC 2 audit is
SOC 2 was developed by the American Institute of Certified Public Accountants (AICPA). It assesses an organisation’s controls against five Trust Service Criteria: security, availability, processing integrity, confidentiality and privacy. A Type II audit checks whether the controls actually worked over a set period.
Kaspersky’s compliance page says the scope covers controls over the antivirus databases behind the regular automatic updates sent to its products. The audit mainly checks that no one can make unauthorised changes while the databases are built and released.
The company has undergone the audit regularly since 2019. Its Global Transparency Initiative website says it last renewed the SOC 2 Type II audit in October 2025.
What Kaspersky says
In the press release, Yuliya Shlychkova, Vice President of Global Public Affairs at Kaspersky, said that for customers and partners the audit is more than a procedural milestone: it is independent confirmation that the security controls behind its technologies remain consistently effective, giving customers confidence in every update and interaction.
The company says regular independent audits are part of its Global Transparency Initiative. Alongside SOC 2, Kaspersky holds ISO/IEC 27001 certification, and its enterprise products hold Common Criteria certifications.
The Russia-based company has faced security questions in several Western countries for years. In June 2024, the US Commerce Department banned sales of Kaspersky software in the country on national security grounds. Kaspersky denied the allegations at the time.
Sources
- Digibangla Tech News, ‘SOC 2 nirikkhay shofol Kaspersky’ (Bangla), 15 November 2026, 4:02 pm, https:/
/ digibangla tech. news/ 195802 - Kaspersky press release, ‘Kaspersky successfully completes SOC 2 audit, demonstrating continued maturity of its security controls’, 4 September 2026, https:/
/ www. kaspersky. com/ about/ press- releases/ kaspersky- successful ly- completes- soc- 2- audit- demonstrat ing- continued- maturity- of- its- security- controls - Kaspersky SOC 2 compliance page, https:/
/ www. kaspersky. com/ about/ compliance – soc2 - Kaspersky Global Transparency Initiative, SOC 2 Type II renewal (October 2025), https:/
/ gti. kaspersky. com/ en/ kaspersky- successful ly- completes- soc- 2- audit - US Bureau of Industry and Security, Kaspersky software prohibition, June 2024, https:/
/ www. bis. gov/ press- release/ commerce- department – prohibits- russian- kaspersky- software- u. s. – customers

Comments