
Alpine/musl OpenSSH password bypass (*sshhole): update now
*sshhole: OpenSSH password bypass on Alpine/musl — update openssh and restart sshd now.
Staff Correspondent
A serious password-authentication bypass in OpenSSH on Alpine Linux and other musl-based systems has been disclosed; researchers call it *sshhole. In a Facebook post at 12:22 pm Dhaka time on 6 November, Aminul Islam highlighted the issue and urged Alpine users to upgrade packages and restart sshd.
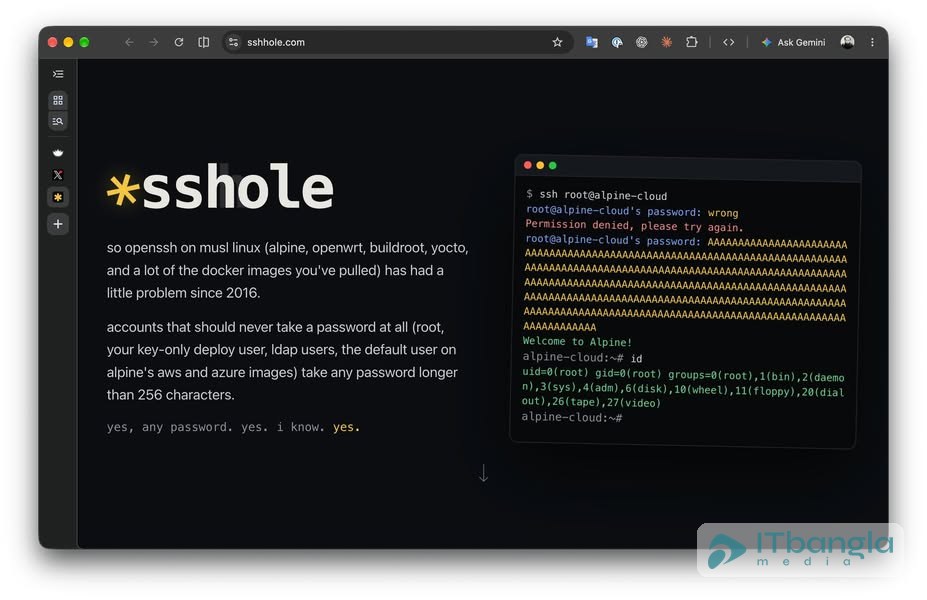
According to Alpine Linux’s security advisory (5 November 2026), when openssh-server is built without PAM and PasswordAuthentication is enabled, accounts whose password field is * may accept a very long password (about 257–1024 bytes) if the system also has at least one valid password hash. It does not affect every distribution—only musl setups under those conditions. Root may still be limited by the default PermitRootLogin prohibit-password, but other login-capable accounts remain at risk.
Aminul’s post said Alpine has already updated the OpenSSH server package. The advised steps are apk upgrade -U -a and rc-service sshd restart. If an update is not possible yet, disabling PasswordAuthentication is recommended. Details: sshhole.com and Alpine’s official advisory.


Comments